Digital Loyalty Cards & Privacy: GDPR, CCPA and You
You want to use a digital loyalty card but aren't sure how it fits with privacy laws like the GDPR or US rules like the CCPA? Understandable. As a business owner, you want loyal customers — but not at the expense of their privacy. This guide answers every question you have about data privacy and digital punch cards. Clear, honest, without legal jargon.
TL;DR
Stempely is GDPR-compliant and privacy-friendly by design. No names, no emails, no phone numbers. Customers remain anonymous. Data hosted in the EU. No data sharing with third parties.
Ironically, handwritten customer lists next to the register are the real privacy risk — more on that below.
Business owners building privacy-friendly customer loyalty
"We used to keep a handwritten customer list next to the register. When I found out that could be a privacy problem, I switched to Stempely right away. Now everything is anonymous and still works."
M. B.
Bakery owner
"My accountant asked me whether our punch cards were privacy-compliant. With Stempely I could show right away: no personal data, hosted in the EU. Case closed."
T. K.
Coffee shop owner
"Push notifications were the sticking point for me. With Stempely everything runs via opt-in and anonymous IDs. My lawyer gave the green light — no concerns."
S. R.
Hair salon owner
Understanding Data Protection
What does a digital loyalty card store?
The most important question first: what data actually ends up on the server when a customer uses your loyalty card?
With Stempely the answer is: as little as possible. When a customer scans your QR code, the following happens:
Anonymous customer ID
A randomly generated ID that cannot be traced back to a person
Stamp count
How many stamps the customer has collected
Reward status
Whether a reward can be redeemed or has already been redeemed
Last visit
When the last stamp was scanned — as a date, without time tracking
Name or real name
Not collected — Stempely never asks for it
Email address
Not collected — no account required
Phone number
Not collected — push runs via anonymous device ID
Location data
No GPS tracking, no geofencing, no movement profiles
In summary: Stempely knows that “Device #A7x9” has 7 stamps at your business. Stempely does not know that the device belongs to Sarah Miller, 34, who lives at 12 Maple Street. And that is exactly the point.
Is Stempely GDPR-compliant — and what about US privacy laws?
Yes — and not because we have a 40-page privacy policy, but because the system is built from the ground up so that it does not need any personal data.
The GDPR applies when personal data is processed — i.e. data that can be attributed to a specific person. Since Stempely works exclusively with anonymous, randomly generated IDs and stores no identifying information, the vast majority of GDPR requirements do not apply. The same logic holds for US privacy laws like the CCPA: they regulate personal information, and Stempely simply does not collect any that identifies your customers.
0
personal data points per customer
DE/EU
hosting — data does not leave the EU
0
third parties with access to customer data
What Stempely specifically does for GDPR compliance:
- Privacy by Design: The system collects no personal data from the outset
- Data minimization: Only the data technically required for the loyalty card
- Hosted in Germany/EU: data stays under GDPR protection
- No data sharing: Neither to advertising partners nor to data brokers
- Opt-in for push: Notifications only with the customer's active consent
- No tracking: No advertising or tracking cookies, no fingerprinting, no movement profiles
Do customers need to give consent?
This is the question that unsettles business owners the most. The short answer: No, no separate consent declaration is required.
Why? Because the GDPR only requires consent when personal data is processed — and US laws like the CCPA likewise focus on personal information. Since Stempely does not collect such data, there is nothing to consent to.
What does happen is an active action by the customer: they scan the QR code — with their phone camera or the Stempely app — save the loyalty card and consciously decide to participate in your loyalty program. This is not passive data collection — it is a voluntary, informed decision.
Comparison: Consent
Classic newsletter system
Email address required. Double opt-in mandatory. Consent declaration to be documented. Right to withdraw to be explained. Retention obligations to be observed.
Stempely digital punch card
No email. No account. No double opt-in. The customer scans, collects stamps, redeems rewards. Done. No consent declaration required.
Where is the data stored?
All Stempely data is hosted on servers in Germany and the EU. Stempely is a German company, and your loyalty data stays in the EU.
Why this matters: the EU has some of the strictest data-protection rules in the world. Hosting under GDPR means your customers' loyalty data is protected to that standard — whether your shop is in Texas, Toronto, Manchester or Sydney. Many other tools are vague about where data lives and who can access it.
Stempely
- Hosted in Germany/EU
- No data sharing with third parties
- GDPR-compliant infrastructure
- No names, emails or phone numbers
Many other tools
- Hosting location often unclear
- Collect names, emails and phone numbers
- Data shared with ad or analytics partners
- Extra contracts and paperwork for compliance
Are paper punch cards better from a data protection perspective?
Many people think so — but the opposite is true.
A paper punch card in itself is data-protection-neutral. It contains no personal data. The problem lies elsewhere: in the practices that develop around it.
What many businesses do on the side (and are not allowed to do):
- Keep handwritten customer lists with names and phone numbers
- Store customer data in unsecured Excel spreadsheets on a laptop
- Collect business cards and use them for marketing without consent
- Create WhatsApp groups with customer numbers
All of these are processing of personal data — and therefore subject to the GDPR and, depending on where you are, to laws like the CCPA. Under GDPR you need a legal basis, a record of processing activities, a privacy policy and the documented consent of each individual customer.
With Stempely none of that happens — no name, no number, no list. A digital loyalty card makes the handwritten customer list unnecessary and thus eliminates the biggest privacy risk in the shop.
Push notifications and data protection
Push notifications are one of the biggest advantages of a digital loyalty card: you can bring back inactive customers, launch flash promotions or remind customers that they are close to their reward. But are push notifications actually privacy-compliant?
Yes — when implemented correctly. And with Stempely that is exactly the case.
Opt-in via the operating system
If a customer uses the Stempely app, iOS or Android explicitly asks: “Can this app send you notifications?” Push notifications are only activated on “Yes.”
Anonymous delivery
The push notification is sent to an anonymous device ID. Stempely knows neither the name nor the email of the recipient. It is technically impossible to attribute the message to a person.
Deactivatable at any time
The customer can deactivate push notifications at any time in the system settings — without deleting the app, without contacting you. Full control with the customer.
Comparison with email marketing: For a newsletter you need the customer's email address, a double-opt-in confirmation, documented consent and a functioning unsubscribe option. With Stempely push you need: none of that. The customer decides via the system setting — and you send to an anonymous ID.
To check off
Checklist: privacy-friendly customer loyalty
7 points you should check as a business owner — whether you use Stempely or not.
No handwritten customer lists
If you collect names and phone numbers on paper, you need a legal basis and the documented consent of each customer.
No unsecured Excel spreadsheets
Customer data in an Excel file on a laptop? Without encryption and access control, that can violate GDPR and US state privacy and data-security laws.
No text or WhatsApp marketing without consent
Group chats or text-message blasts to customers need documented consent — under GDPR, and in the US under rules like the TCPA for marketing texts.
Display privacy policy in the shop
If you process personal data (e.g. for a newsletter), a privacy policy must be available.
Maintain a record of processing activities
Under GDPR, companies must document what data they process. With Stempely the entry is minimal, since no personal customer data is collected.
Push notifications only with opt-in
Notifications to customers may only be sent if the customer has actively agreed. With Stempely the operating system handles this automatically.
Know where your data is hosted
If you use digital tools, find out where the data lives and who can access it. Stempely hosts everything in Germany/the EU — no sharing with third parties.
No contract · No credit card · Set up in 5 minutes
Data protection meets customer loyalty
Privacy-friendly — and you still see everything
Anonymous data does not mean less insight. You see stamps, rewards and activity — without ever knowing a name.
1.281
Total customers
6.316
Total stamps
3.114
Redeemed rewards
Live
Stamps today
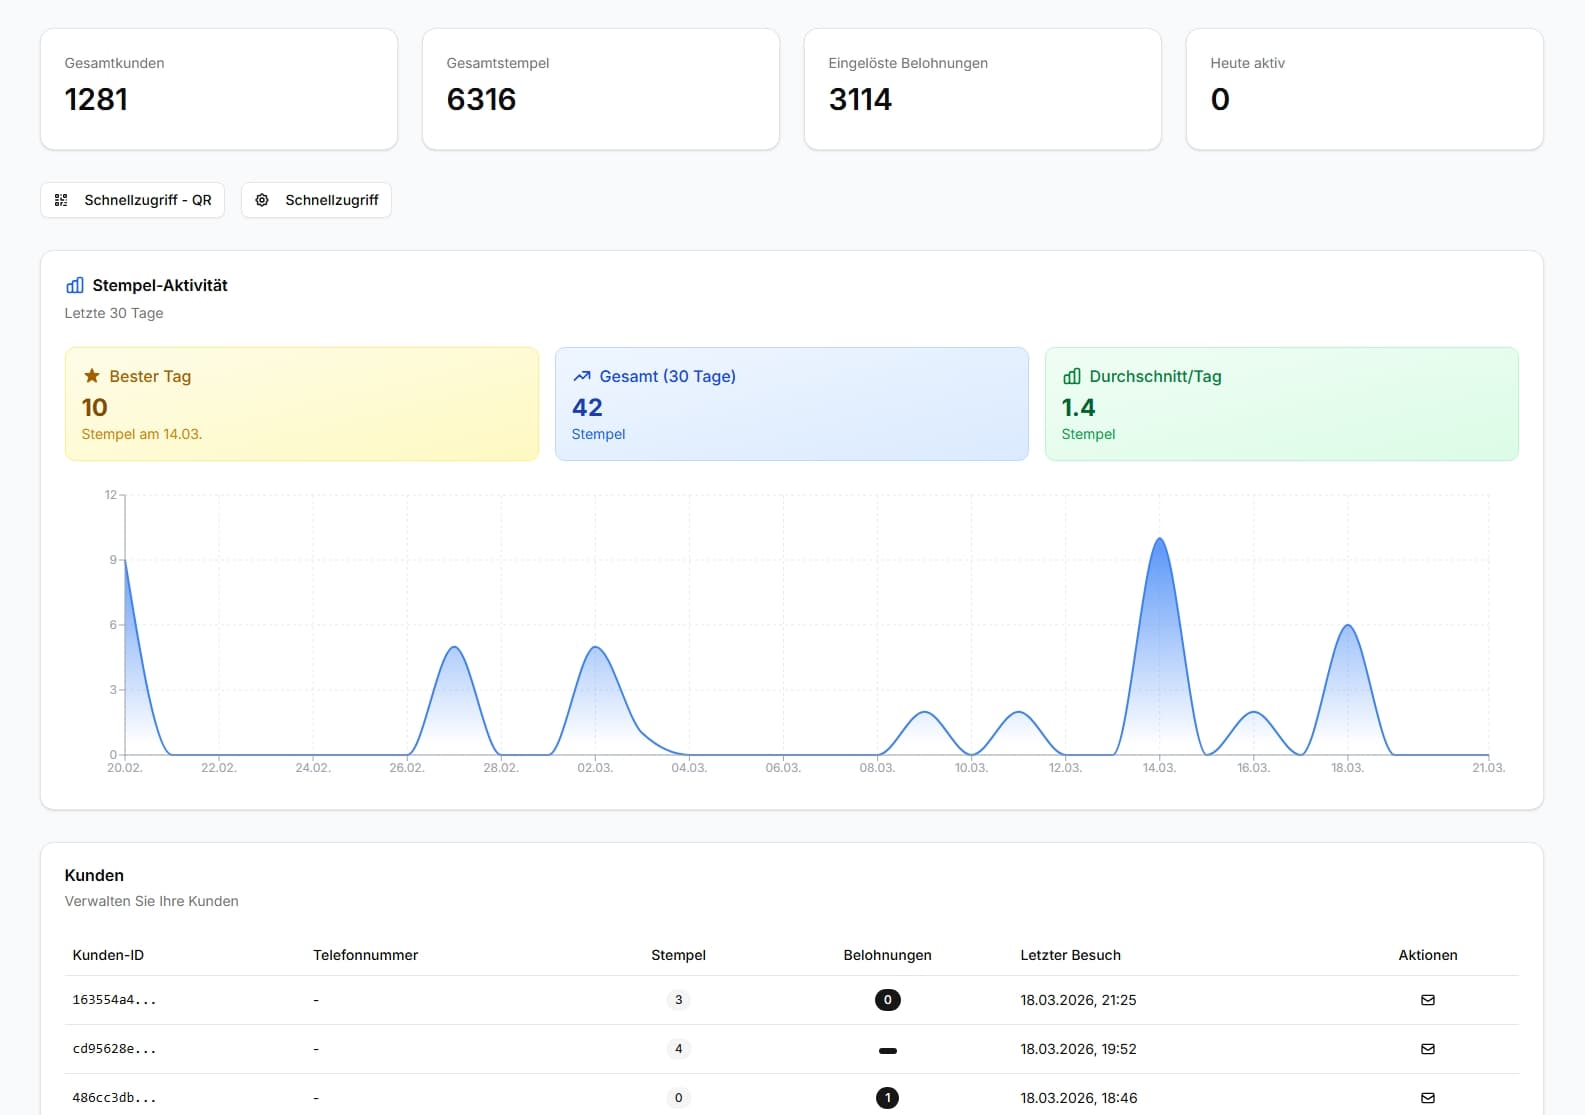
Real production data. All customers anonymous — no names, no emails, no phone numbers visible.
Choose Your Plan
All features free for up to 25 customers. Then Premium.
Stempely
- Up to 25 customers
- Digital loyalty card
- QR code scanner
- Contactless stamps (NFC)
- Send offers & reminders
- Statistics
- QR code with logo
- Customer list
- More visibility with web
- Priority support
Franchise
- Everything in Premium
- Multiple locations
- Custom terms
- Dedicated account manager
All prices incl. VAT.
8 frequently asked questions: digital loyalty cards & privacy
What personal data does Stempely store?
Stempely stores no personal data such as names, email addresses or phone numbers. Customers are identified exclusively via an anonymous, randomly generated ID. As a business owner you only see: stamp count, reward status and last visit — without knowing exactly who the person is.
Do I need a consent declaration from my customers?
Since Stempely does not process personal data, no separate consent declaration is required. Scanning the QR code — whether with the phone camera or in the Stempely app — is an active, voluntary action by the customer. There is no tracking and there are no advertising cookies. Anyone who saves the card via Apple Wallet or Google Wallet receives a single cookie in the browser that only recognizes their loyalty card — without a name, without an email address.
Where is Stempely data stored?
All data is hosted on servers in Germany and the EU, under GDPR. Stempely is a German company; the data does not leave the EU.
Are paper punch cards harmless from a data protection perspective?
No, on the contrary. Many businesses keep handwritten customer lists with names and phone numbers on the side — this is processing of personal data and requires a legal basis under GDPR (and can fall under US laws like the CCPA). Paper punch cards themselves are data-protection-neutral, but the surrounding practice often is not.
Does Stempely share data with third parties?
No. Stempely does not sell, share or transfer customer data to third parties. Your business data and the anonymized stamp data belong to you. There are no advertising partners, no data brokers and no tracking by third-party providers.
How do push notifications work in a data-protection-compliant way?
Push notifications are only sent if the customer has actively allowed them in the app (opt-in via the operating system). The message is sent to an anonymous device ID — Stempely knows neither the name nor the email of the recipient. Customers can deactivate notifications at any time in the system settings.
Do I as a business owner need to maintain a record of processing activities?
If GDPR applies to your business (for example in the EU or UK), yes — companies must maintain a record of processing activities under Art. 30 GDPR. However, since Stempely does not process personal customer data, the entry is minimal. Processing is limited to anonymous stamp data and your own business data (login, email).
Can I use Stempely without customers installing an app?
Yes. Customers can save their loyalty card directly to Apple Wallet or Google Wallet without an app — likewise without an account, without an email address and without a name. Alternatively, there is the free Stempely app, also without an account and without personal data, but with push notifications. In both cases, the customer actively decides whether they want to participate.
"My accountant gave the green light — no personal data, hosted in the EU. Case closed."
— T. K., coffee shop owner
Privacy-friendly customer loyalty. Starting today.
No personal data, no consent declarations, no customer lists on paper. Your digital loyalty program is live in 5 minutes.
The free plan stays free — no expiry date, no tricks.
Start now — no contract, no credit cardFree to start · GDPR-compliant · Hosted in the EU
Also available directly as an app